Chrome suspicious site warnings are becoming clearer as Google separates sites that may be risky from pages that are already classified as dangerous. The change is meant to give people more useful context before they continue, while stronger AI-assisted checks remain available through Enhanced Protection.
Google described the update in its Security Blog on October 20, 2026. The announcement focuses on evolving web scams rather than a single campaign. It explains how deceptive pages can change quickly, imitate legitimate services and use social engineering steps that traditional reputation systems may not catch immediately.
Chrome suspicious site warnings: what changed
The browser now makes a clearer distinction between a suspicious site and a dangerous one. A suspicious warning signals that Chrome has detected indicators that deserve caution but may not yet justify the strongest block. A dangerous warning is reserved for pages that Chrome has classified with higher confidence. This distinction matters because it avoids presenting every uncertain signal as an identical threat while still interrupting risky browsing.
Google says the protection is especially relevant to fast-moving scams. Attackers can rotate domains, rewrite page text and change visual elements before conventional blocklists are updated. A warning delivered at the point of navigation gives users a chance to stop before entering a password, downloading a file or following instructions that change device settings.
How Enhanced Protection uses fresh signals
Users who enable Enhanced Protection receive additional real-time checks. Google says a server-side Gemini model can examine signals from pages that have not been seen before. The company also describes the use of ephemeral page text for detection, meaning the protection can evaluate relevant text without turning the feature into a permanent archive of everything a person reads.
That does not make the browser infallible. A page can still be new enough to evade detection, while a legitimate site may occasionally appear unusual. Chrome suspicious site warnings should therefore be treated as a decision aid, not as proof that every unflagged page is safe. Domain spelling, download provenance and the context of a login request still need independent verification.
ClickFix scams are a specific target
Google explicitly calls out ClickFix-style attacks. These pages claim that something is broken and instruct the visitor to copy and run a command, often in a terminal or operating-system dialog. The command may download malware or change security settings. The scam succeeds by convincing the victim to perform the sensitive action voluntarily, which can bypass some automatic safeguards.
A legitimate website rarely needs a visitor to paste an unexplained command to verify a browser session, solve a CAPTCHA or restore video playback. If a page asks for that step, close it and navigate to the service through a known bookmark or manually typed address. Do not rely only on the padlock icon, because HTTPS encrypts a connection but does not prove the operator is trustworthy.
What users should do after a warning
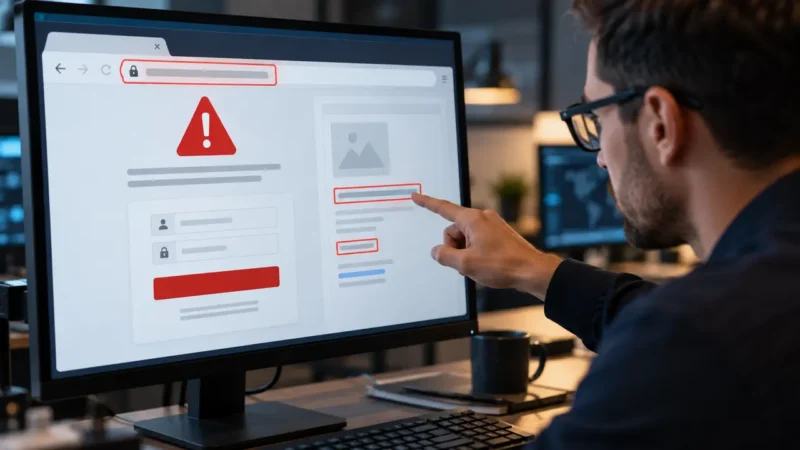
Do not bypass the warning simply because the page looks familiar. Check the complete hostname, not just the first word, and compare it with the organisation’s official domain. If the page came from an advertisement, message or QR code, open the service independently. People who already entered a password should change it from a clean device, revoke active sessions and enable phishing-resistant multi-factor authentication where available.
Downloaded files deserve a separate check. Confirm the publisher, signature and expected hash when the vendor publishes one. A genuine signed installer does not validate the website or form that appeared before it. SajberSfera previously explained this distinction in its analysis of a fake VPN download site that stole administrator credentials before serving a legitimate client.
Privacy and practical limits
Enhanced Protection is optional, and users should review the setting before enabling it. Google’s description explains the security purpose, but organisations may still need to assess the feature against their own privacy, compliance and browser-management policies. Managed environments should test the warning flow so employees know when to stop and how to report a suspicious page without taking screenshots that expose sensitive data.
Chrome suspicious site warnings reduce ambiguity at an important moment, but they do not replace cautious navigation. The most reliable defence remains layered: updated browsers, verified bookmarks, password managers that refuse to fill credentials on the wrong domain, strong account protection and a reporting path that lets security teams react quickly.